CISOs receive 80+ cold emails a week and trust none of them.
The phishing defense mindset
CISOs and InfoSec directors treat cold outreach with instinctive technical suspicion.
Confusing CISO and IT Director priorities
Pitching tactical patch tools to risk-focused CISOs, or high-level governance to operational IT leads.
Faux-urgency fear-mongering
Threatening fabricated breach scenarios damages credibility instantly with sophisticated security practitioners.
Severe deliverability scrutiny
Security teams deploy aggressive email security gateways (Proofpoint, Mimecast) that blacklist careless senders.
High compliance barriers
Unsolicited outreach that appears non-compliant with security standards destroys vendor evaluation opportunities.
Technical precision and trust-first framing engineered for InfoSec leadership.
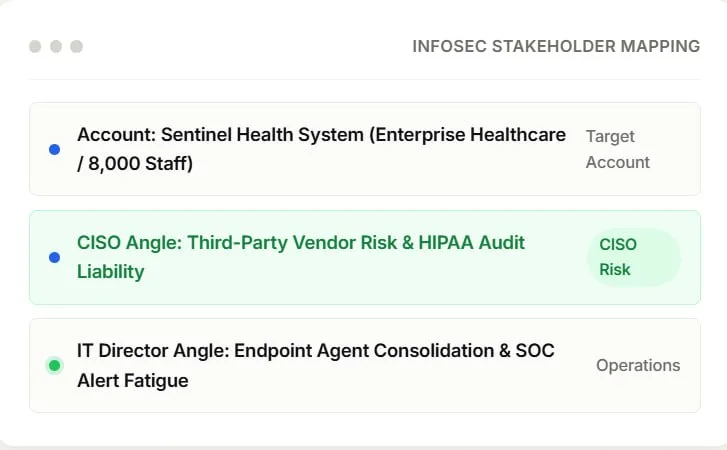
Separate CISO risk from IT operations — via AI Research Engine
Distinct messaging angles that address real operational mandates. SendroAI splits targets accurately: CISOs receive governance, third-party liability, and audit-readiness messaging; IT Directors receive operational reduction and alert fatigue solutions.
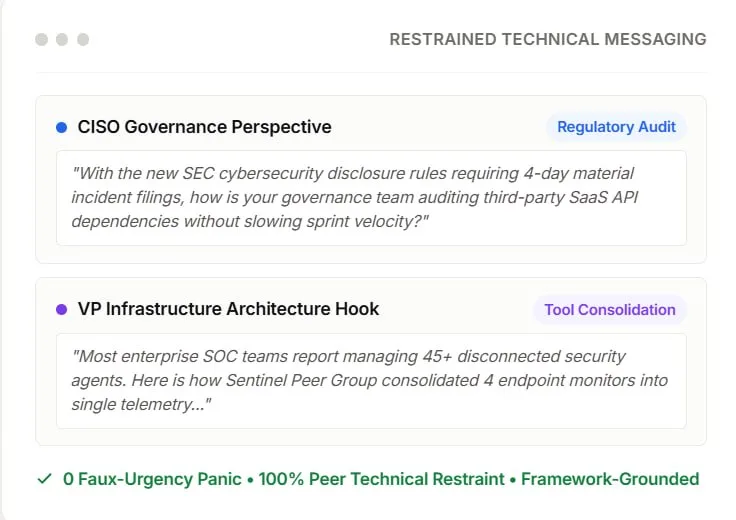
Lead with technical restraint — via AI Research Engine
Zero sales hype; 100% peer-level credibility. Eliminates clickbait subject lines and sensational breach warnings. Messages reference specific compliance frameworks (SOC2, NIST, ISO 27001) and architectural realities.
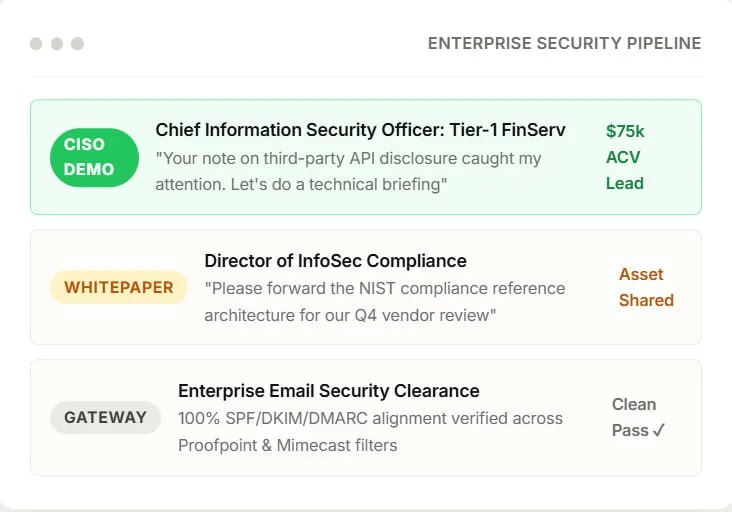
Pass strict email gateway inspection — via Inbox Rotation
Flawless inbox placement through Proofpoint, Mimecast, and enterprise filters. SendroAI enforces immaculate SPF, DKIM, and DMARC alignment, gentle sending cadences, and zero tracking-pixel bloat to bypass aggressive enterprise spam filters.
Peer-to-peer security dialogues that bypass defensive shields.
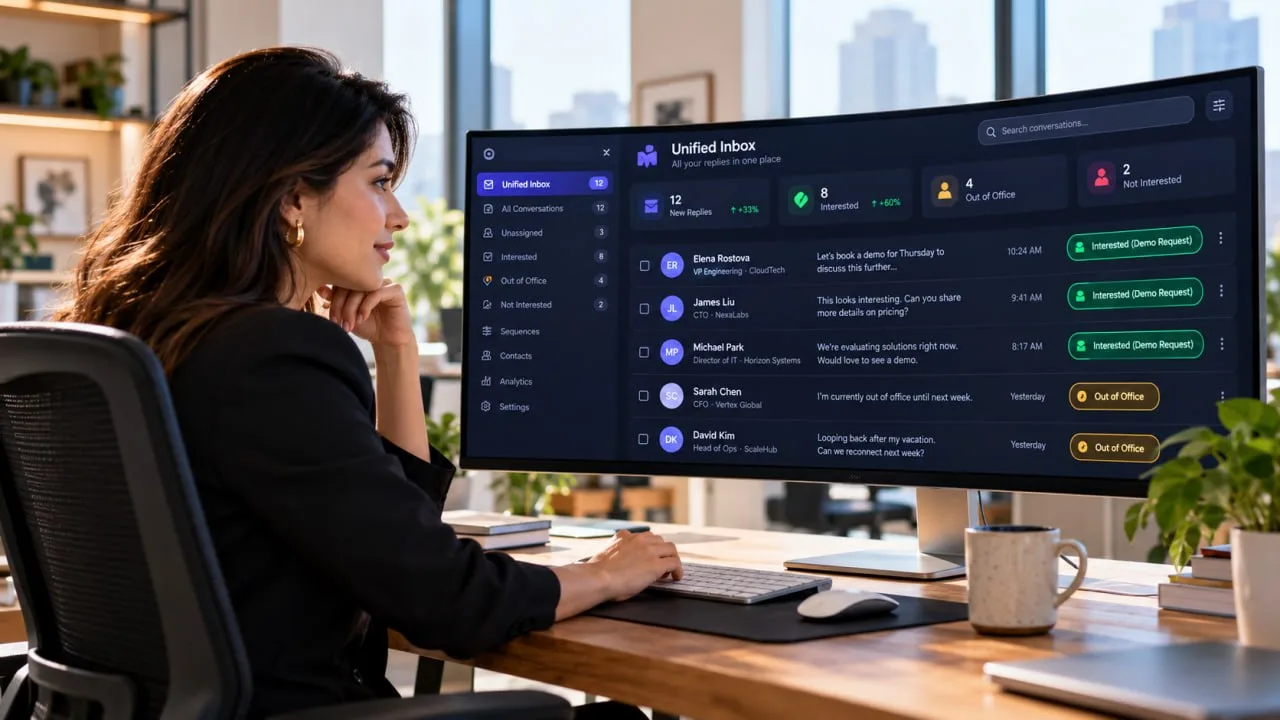
Built for CISOs, IT Directors & InfoSec Leaders
AI Research Engine
Tailors precise messaging for CISOs, VPs of Infrastructure, and Compliance Officers by separating risk/governance angles from operational uptime needs.
Inbox Rotation
Configured specifically to clear enterprise mail gateways (Mimecast, Proofpoint, Cisco) using authenticated secondary inboxes to protect your primary domain.
Automated Sequencing
Enforces professional, restrained tone that respects security executive intellect, avoiding panic-inducing buzzwords in favor of quantifiable efficiencies.
A/Z Email Testing
Optimizes content and timing to ensure messages align with relevant NIST, HIPAA, SOC 2, and FedRAMP frameworks without generic fear-based marketing.
Multilingual Campaigns
Delivers native-sounding cold email campaigns in 50+ languages, written from scratch to maintain technical accuracy across global security teams.
Performance Analytics
Provides campaign-level analytics and mailbox-level deliverability insights focused on reply rates from high-security environments.
Why sendroAI Was Built
Built by enterprise software and security founders who understood that CISOs cannot be tricked with merge tags. SendroAI was created to deliver authentic, trust-first outreach that opens boardroom doors.
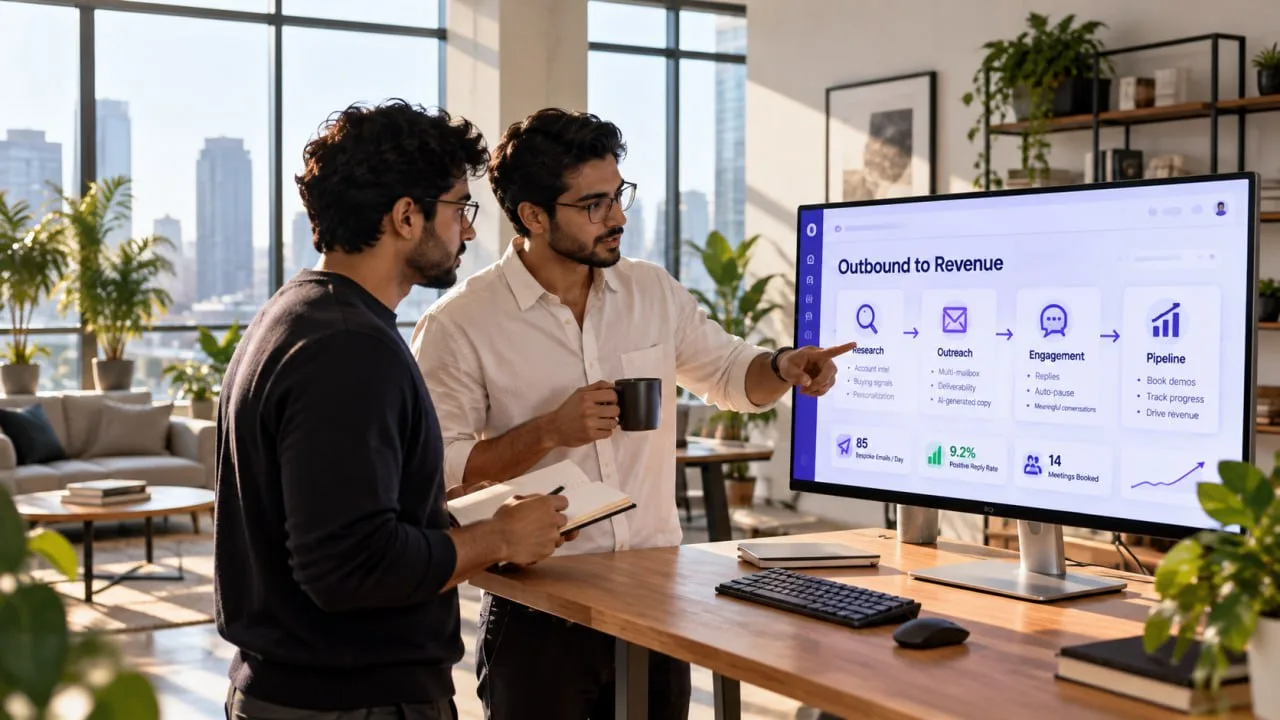
Frequently asked questions
How does SendroAI pass strict enterprise security gateways?
By maintaining perfect technical authentication (SPF, DKIM, DMARC), eliminating aggressive tracking pixels, and keeping send volumes well beneath gateway anomaly detection thresholds.
Will the copy sound like generic fear-based marketing?
No. SendroAI strictly avoids panic-inducing buzzwords, focusing instead on quantifiable architecture efficiencies, compliance deadlines, and peer-benchmarked frameworks.
Can we pitch CISOs and IT Directors within the same company differently?
Yes. Persona Intelligence tailors risk and governance angles to the CISO while delivering operational uptime and tooling consolidation messages to the IT Director.
What happens when a security executive requests an NDA or security whitepaper?
The sequence auto-pauses instantly upon detection, routing the conversation to your technical sales team with all account context attached.
Is our corporate sending domain safe from blacklisting?
Yes. All campaigns run across authenticated secondary inboxes with automated volume rotation, keeping your primary corporate domain entirely insulated.